PT 220 ISO/IEC 27001:2022 Internal Auditor Training Course
Approved by:
This ISO 27001 Internal Auditor Course aims to provide learners with the knowledge and skills required to perform an internal audit of part of an information security management system based on ISO/IEC 27001:2022 and applicable international regulatory standards, and to report on the effective implementation and maintenance of the management system in accordance with ISO 19011:2026. Note: This document references ISO/IEC 27001:2022 as the information security, cyber security and privacy protection management system standard that provides the context for the internal audit. However, this course does not address ISO/IEC 27001:2022 in detail and does not aim to equip learners with the knowledge and skills to determine conformity, or otherwise, with ISO/IEC 27001:2022. Learners requiring the knowledge and skills to conduct an entire information security, cyber security and privacy protection management system audit against ISO/IEC 27001:2022 should be directed to attend a CQI and IRCA or Exemplar Global Certified IEC 27001:2022 Lead Auditor (PR373).
Loading sessions...
More
You can choose the curriculum & training that fits your needs
Answer a few quick questions, and we'll match you with tailored training recommendations designed for your career stage and industry.
Prior Knowledge Requirements
This course aims to provide learners with the knowledge and skills required to perform an internal audit of part of an information security management system based on ISO/IEC 27001: 2022 (or equivalent) and report on the effective implementation and maintenance of the management system in accordance with ISO 19011:2026. (Note: this document references ISO/IEC 27001 as the management system standard that provides the context for the internal audit. However, this course does not address ISO/IEC 27001:2026 in detail and does not aim to equip learners with the knowledge and skills to determine conformity, or otherwise, with ISO/IEC 27001:2022. Learners requiring the knowledge and skills to conduct entire information security management system audits against ISO/IEC 27001:2022 should be directed to attend a CQI and IRCA or Exemplar Global Certified ISO/IEC 27001:2022 Lead Auditor (ISMS) Training course.)
Learners who successfully complete this ISO/IEC 27001: 2022 Internal Auditor (ISMS) course will satisfy part of the training requirements for initial certification as an IRCA Internal ISMS Auditor. In addition to this course, learners must also complete a CQI and IRCA Certified ISO/IEC 27001:2022 Foundation (ISMS) Training course to meet the full training requirements for initial certification as a CQI-IRCA or Exemplar GlobalInternal ISMS Auditor.
Virtual Technology Requirements
To participate in the virtual training sessions, you will need:
- Workplace Networks & VPN Connections
- In our experience, Workplace IT environments’ internal configurations and available software can vary (new or old), and there may be various limitations or other restrictions in place, and as such, the functionality of any Learning Management System (LMS) may be impacted, restricted, and may not perform well.
- The use of a VPN connection can result in poor performance and interfere with the SSO (Single Sign On) that connects users from our website and associated applications to their eLearning modules. We strongly recommend ensuring you are disconnected from a VPN or Proxy Server if experiencing any issues with accessing the eLearning modules.
- Recommended Operating Systems
- Windows 7/10, macOS Sierra, iPad iOS 10
- Mobile Devices
- The Kelmac Group Academy LMS is not available on a mobile app at this time. We recommend using a web browser on a mobile device to complete any eLearning modules. However, if completing any final assessment, we recommend completing it via a desktop browser.
- Internet Speed & Reliability
- We recommend using an internet connection of 256 Kbit/sec or faster, which will ensure that you can successfully access our eLearning modules. A stable connection is important to ensure you do not experience any outages during the completion of any module or any final assessment (s).
- Recommended Internet Browsers
- Google Chrome 32-bit version 50 or later (most recommended)
- Safari 10 or later
- Note: Add-ons and toolbars can affect any browser’s performance.
- Recommended Settings
- We recommend that the following settings be enabled:
- Cookies
- Pop-ups (in both Internet browsers and security software)
- JavaScript
- Plugins
- Latest Version of Adobe Flash Player
- Latest Version of Adobe Acrobat Reader
- To view all resources made available within our LMS, you will probably need Microsoft Office (Word, Excel, PowerPoint) or an equivalent (i.e, Open Office, Viewer) installed.
- Virtual Learning Technology Requirements
- General
- Laptop or desktop computer (Note: A tablet or mobile device is not suitable for this training)
- Advisory: Certain features ONLY work on the laptop/desktop version & each Learner will be required to actively participate in online exercises/assignments via virtual breakout rooms in groups
- Webcam – Built-in or USB plug-in
- Advisory: This is required to be enabled for the duration of any live or group exercises, as 100% attendance & participation are required on all virtual workshops. We must be able to verify attendance during live sessions and during any virtual breakout sessions.
- Speakers and a microphone – Built-in or USB plug-in. We strongly recommend a headset for this training.
- Advisory: A headset will ensure that each Learner can effectively communicate & listen. Plus, a headset will provide a better filter for any background noise or interference that may impact the Learner experience, and that of other Learners.
- Internet connection – Minimum of 1.0 Mbps
- Advisory: Naturally, each Learner should ensure that they have reliable access to the Internet during the training, either through a suitable Wi-Fi or wired connection. Any disruptions may cause difficulties during the training and, in certain cases, if large portions of the training are missed, a Learner may not be able to complete the program (Certification Criteria may not be met).
- Zoom Workday
- This is the platform we use for video and team collaboration. Approximately 1 week in advance, a calendar invite including a link to access training material where the course documentation & resources are located. This team’s environment will also be used for submitting/sharing completed individual and team-based assignments.
- We will be sharing access with the EMAIL ID that was provided to us when each Learner was registered for the course.
- It is important that each Learner verifies that they can access the Zoom Workday platform successfully in advance of the live workshops to avoid delays or their planned attendance being impacted by not being able to access the Zoom Wokrday platform during the training.
- For support with accessing the Zoom Platform, please contact one of our representatives for assistance in advance of the start date to ensure you can gain access on the date of your training.
- Mimeo DRM Application - Digital Course Material
- This is the platform we use for distributing digital versions of course material, ISO standards, case study material, and reference material. Please note International standards are subject to international copyright laws and are not available to download or print.
Course Overview
The ISO 27001 Internal Auditor Course aims to provide delegates with the knowledge and skills required to perform an internal audit of part of an Information Security, Cyber Security and Privacy Protection Management System based on ISO/IEC 27001:2022 and report on the effective implementation and maintenance of the management system in accordance with ISO 19011:2026. Note: ISO/IEC 27001:2022 is the Information Security, Cyber Security, and Privacy Protection Management System standard that provides the context for the internal audit. However, this course does not address ISO/IEC 27001:2022 in detail and does not aim to equip delegates with the knowledge and skills to determine conformity, or otherwise, with ISO/IEC 27001:2022. Delegates requiring the knowledge and skills of how to apply ISO/IEC 27001:2022, Information Security, Cyber Security and Privacy Protection Management System – Requirements, should attend a CQI and IRCA or Exemplar Global Certified ISO/IEC 27001:2022 Foundation training course before attending a CQI and IRCA or Exemplar Global Certified ISO/IEC 27001:2022 Internal Auditor or Auditor/Lead Auditor training course.
Learning Objectives
Knowledge
With reference to the Plan-Do-Check-Act (PDCA) cycle, explain the process-based information security management system model for ISO/IEC 27001:2022, and the role of internal audit in the maintenance and improvement of information security management systems.
Explain the role and responsibilities of an auditor to plan, conduct, report, and follow up an information security management system internal audit in accordance with ISO 19011:2026.
Skills
Plan, conduct, report, and follow up an internal audit of part of an information security management system based on ISO/IEC 27001:2022 and in accordance with ISO 19011:2026, as covered in the ISO 27001 Internal Auditor Course.
Our Methodology
Introducing our skilled Consultants!
Gerard Kelly
Principal Consultant
Syllabus breakdown
Introduction and Welcome
- Course Introduction and Welcome
- Course Certification
- Course Learning Objectives
- Course Program/Rules
- Auditor Certification
- Privacy, Data Processing, Special Considerations,
- Course Materials
- Virtual Platform Overview
- Learner Support
Introduction to ISO/IEC 27001:2022
- Purpose and Benefits of an Information Security, Cyber Security and Privacy Protection Management System
- ISO/IEC 27001:2022 Overview and Structure
- Management System Principles and their relevance
- ISO/IEC 27001:2022 Process Model
- ISO/IEC 27001:2022 Key Concepts
- ISO/IEC 27001:2022 Terminology
- ISO/IEC 27001:2022 Requirements [Overview only]
ISO 19011:2026 Purpose, Scope and Requirements
- Overview and Context
- Introduction, Scope and Structure
- Terminology
- Audit Principles
- Audit Program
- Audit Life Cycle
- Auditor Roles and Responsibilities
- Auditor Behaviors
- Auditor Competency, Evaluation and Performance
Audit Initiation and Planning
- Audit Initiation
- Audit Risks and Opportunities
- Audit Plan Exercise
- Audit Checklist Exercise
Conducting the Audit
- Audit Meetings
- Opening Meeting Role Play Exercise
- Audit Evidence
- Audit Findings
- Collecting Audit Evidence Exercise
Audit Reporting
- Audit Conclusion Statement/Audit Report
- Closing/Exit Meeting Role Play Exercise
- Audit Post-Delivery Activities
- Extent Analysis, Root Cause Analysis, Correction, Corrective Action
Class Close
- Summary/Review of Learning Objectives
- Training Certificate
- Class Evaluation
- Class Close
Frequently Asked Questions
Yes, this is a CQI-IRCA Certified Internal Auditor Training Course under Course ID 2604. The course is aligned to recognised Internal Auditor learning requirements for ISO/IEC 27001:2022. Successful completion supports learners who are seeking to meet the training requirement for CQI-IRCA Internal ISMS Auditor registration, subject to the CQI-IRCA registration criteria in force at the time of application.
This course is intended for professionals who need to plan, conduct, or participate in first-party internal audits of an Information Security Management System, known as an ISMS, against ISO/IEC 27001:2022. It is suitable for individuals responsible for auditing a process, activity, department, or function within an organisation’s ISMS, rather than carrying out a full third-party certification audit. Learners should have a basic understanding of ISO/IEC 27001:2022, which may be gained through prior workplace exposure, existing ISMS knowledge, or successful completion of a Fundamentals course.
Yes, learners should already be familiar with the requirements of ISO/IEC 27001:2022, or should have successfully completed a Fundamentals course beforehand. This is a recommended prerequisite for attending the course, as it provides the essential background knowledge needed for Internal Auditor training. Having this prior understanding will help ensure that you can fully engage with the audit lifecycle activities covered during the course, including planning, conducting, reporting, and following up internal audits.
This course is the right level if your goal is to become competent to perform internal ISMS audits against ISO/IEC 27001:2022. The course is practical and skills-based, covering audit planning, evidence gathering, findings writing, and reporting. If you are completely new to ISO/IEC 27001:2022, a Fundamentals course may be the best first step before progressing to Internal Auditor training.
• The delivery format for your course will be confirmed at the time of registration. If your cohort is delivered virtually, the training will take place on the Zoom platform, and you will receive the relevant joining instructions, access details, and platform guidance in advance. To participate effectively, you will need a stable internet connection and a laptop, desktop, iPad, or other tablet device that supports the required platform, together with working audio and an active web camera.
The course is practical and interactive, with a strong focus on applying audit methods in realistic ISMS audit scenarios. It includes consultant-facilitated activities aligned to the ISO 19011 audit lifecycle. There is also a strong emphasis on auditor behaviours, audit tools, and evidence-based evaluation throughout the programme.
No, this Internal Auditor course does not include a final written or online certification exam. Instead, the learning consultant carries out regular in-class assessment during the course through activities, participation, and performance evaluation. Full attendance is required, and successful completion is based on attendance together with satisfactory in-class assessment outcomes.
• After completing the course, you will be able to plan and conduct internal ISMS audits against ISO/IEC 27001:2022 for a process, activity, department, or function within an organisation. You will also be able to gather, verify, and evaluate objective evidence using a range of audit methods, rather than relying on interviews alone. In addition, you will be able to write clear audit findings and contribute effectively to audit reporting and follow-up activities.
• You will receive structured learning materials, including access to the relevant standards and content aligned to Internal Auditor competence development. You will also be provided with practical audit tools and templates, such as audit plans, audit scope documents, and audit protocols or checklists, to support the learning process. The course also includes scenario-based exercises designed to help you develop confidence in evidence gathering, writing audit findings, and contributing to audit reporting.
This course places a strong focus on process effectiveness and how ISMS performance links to organisational controls, risk management, and information security outcomes. It develops auditor capability using wider audit methods, including interviews, document review, and analysis of data and records. The course follows a practical, structured approach aligned to the ISO 19011 audit lifecycle, rather than relying on theory alone.
An ISO/IEC 27001 Internal Auditor course provides the knowledge and practical skills needed to initiate, plan, conduct, document, and audit follow up internal audits of an Information Security Management System (ISMS). The training provides participants with an understand ISO/IEC 27001:2022 and ISO/IEC 27002:2022 requirements and apply systematic best internal auditing practices based upon ISO 19011:2026.
ISO/IEC 27001:2022 Internal Auditor training typically provides an overview of the requirements of ISO/IEC 27001:2022 and ISO/IEC 27002:2022, ISMS auditing principles, audit planning and preparation, gathering audit evidence, audit sampling, audit methods, evaluating conformity, identifying and documenting conformities/nonconformities, audit reporting, corrections and corrective actions, and audit follow-up activities as recommended by ISO 19011:2026.
The course develops practical skills for conducting effective ISO/IEC 27001 internal audits, including audit initiation, preparing audit plans and related risks and opportunities, reviewing processes and documented information, collecting and evaluating objective evidence, Audit sampling, evaluating audit findings, documenting conformities/ nonconformities, and supporting correction/corrective actions and audit follow-up. Essentially this course educates and equips participants with the knowledge and skills to conduct internal ISO/IEC 27001 audits based upon the guidance in ISO 19011:2026.
Yes. The ISO/IEC 27001 Internal Auditor course can be suitable for information security professionals, IT personnel, compliance and risk professionals, internal auditors, managers, consultants, and others involved in implementing, maintaining, or auditing an Information Security Management System. It should be emphasised that the adoption of an ISMS is company wide and it affects Information Asset Owners, Audit and Risk committees, C-Suite leaders and Compliance professionals.
Completing an ISO/IEC 27001 Internal Auditor course is an Internationally recognised qualification recognised by industry, IAF Certification Bodies, Government organizations responsible for meeting Regulatory information security, cyber security and privacy requirements. It can strengthen your understanding of ISO/IEC 27001:2022 and ISO/IEC 27002:0222 and develop practical skills for auditing an ISMS. It can help professionals identify conformities/nonconformities, evaluate information security controls and processes, support corrections/corrective actions, and contribute to the continual improvement of an organization's information security management system.
Virtual Technology Requirements
To participate in the virtual training sessions, you will need:
- A current generation laptop or desktop computer with the latest web browser installed, capable of handling multiple software applications at the same time (a tablet or mobile device is not suitable for this training).
- HD webcam (built-in or USB plug-in).
- Speakers and a microphone (built-in or USB plug-in). A headset is highly recommended for optimal audio quality.
- Internet connection with a minimum of 2.5 Mbps download and 3.0 Mbps upload.
- Two display monitors are highly recommended: one for joining the virtual classroom and viewing e-course documentation (if applicable), and the other for completing class exercises and assignments.
Similar Courses
FD 134 ISO/IEC 27001:2022 Foundation Training Course
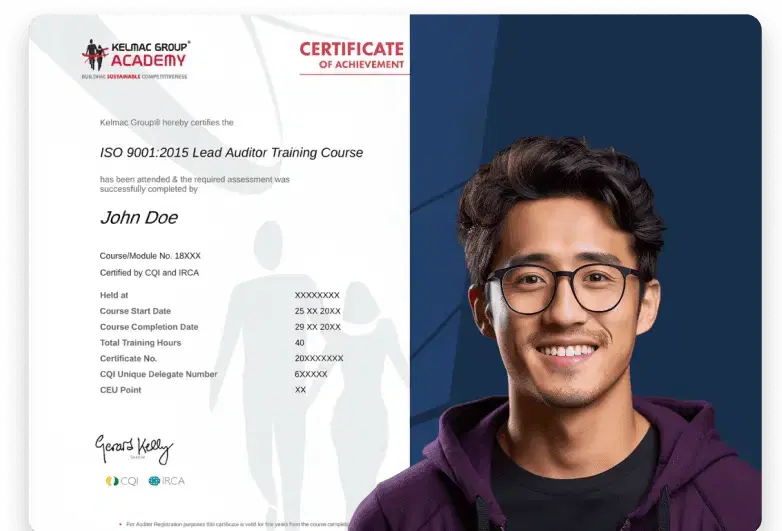
View Sample Certificate of Completion
Upon successful completion, each learner shall receive a digital Certificate of Completion that is recognized globally.