NIS 2.0 Compliance
What is NIS2 The NIS2 Directive (EU 2022/2555) represents a fundamental shift in how cybersecurity is governed across Ireland and the European Union. It expands the scope of regulated sectors, introduces strict supervisory oversight, and places direct accountability on senior management. For organizations operating in regulated or critical sectors, NIS2 is not simply a compliance obligation, it is a regulatory expectation that cybersecurity risk is actively governed at board level. Across Ireland and the EU, regulators expect organizations to evidence not only compliance, but maturity, consistency, and continuous improvement in cybersecurity practices.
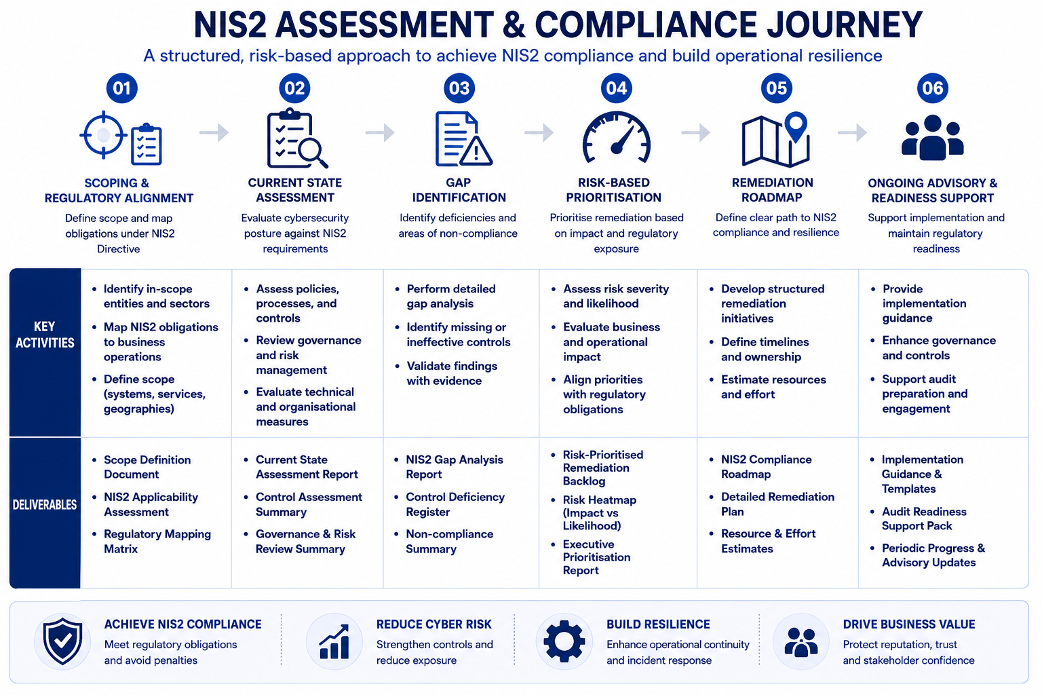
Kelmac Group®’s NIS2 Compliance Services support organisations in assessing their current cybersecurity position, identifying gaps and developing a structured path towards applicable NIS2 requirements. Support can include scope and applicability review, current-state assessment, gap analysis, risk-based prioritisation, remediation planning and implementation guidance. As part of NIS2 Consulting, the focus is on translating regulatory requirements into practical technical, operational and organisational measures that reflect the organisation’s risk profile and operating environment. This provides management with clearer visibility of compliance priorities, responsibilities and the evidence required to demonstrate progress.
Understanding the NIS2 Directive
The NIS2 Directive, formally Directive (EU) 2022/2555, establishes measures intended to achieve a high common level of cybersecurity across the European Union. It introduces cybersecurity risk-management and incident-reporting obligations for entities within its scope, together with requirements concerning supervision and enforcement. For affected organisations, NIS2 requires more than documenting cybersecurity policies. Appropriate and proportionate technical, operational and organisational measures must be implemented to manage risks to network and information systems. Management bodies also have specific responsibilities for approving and overseeing cybersecurity risk-management measures.
Kelmac Group uses the Cyber Fundamentals (CyFun) Framework as the core model for assessing cybersecurity maturity. CyFun provides a structured, measurable framework that translates complex regulatory requirements into practical, assessable domains. It enables organisations to evaluate their cybersecurity posture using a consistent maturity scale and clearly defined control areas. For organisations operating across Ireland and the EU, this structured approach is essential to demonstrate consistency and control effectiveness in line with NIS2 expectations.
CyFun provides a practical way for organisations to translate NIS2 requirements into measurable cybersecurity actions. It aligns governance, risk management, incident response, supply chain security, and resilience capabilities directly with key NIS2 obligations, particularly Articles 20 and 21. By structuring these areas into a clear maturity model, organisations can assess gaps, demonstrate accountability, and build audit-ready evidence. At the same time, CyFun is mapped to globally recognised standards such as NIST Cybersecurity Framework and ISO/IEC 27001, ensuring that improvements made for NIS2 also strengthen overall cybersecurity posture in line with international best practice.
A NIS2 CyFun Maturity Assessment can provide a structured way to examine cybersecurity measures and identify areas requiring further development. The CyberFundamentals (CyFun®) Framework was developed by Belgium’s Centre for Cybersecurity and incorporates controls derived from recognised frameworks and standards, including NIST CSF and ISO/IEC 27001/27002. The framework provides Small, Basic, Important and Essential levels and can support organisations in assessing and improving cybersecurity maturity over time. CyFun can also be used in the context of demonstrating implementation of NIS2 cybersecurity requirements in Belgium.
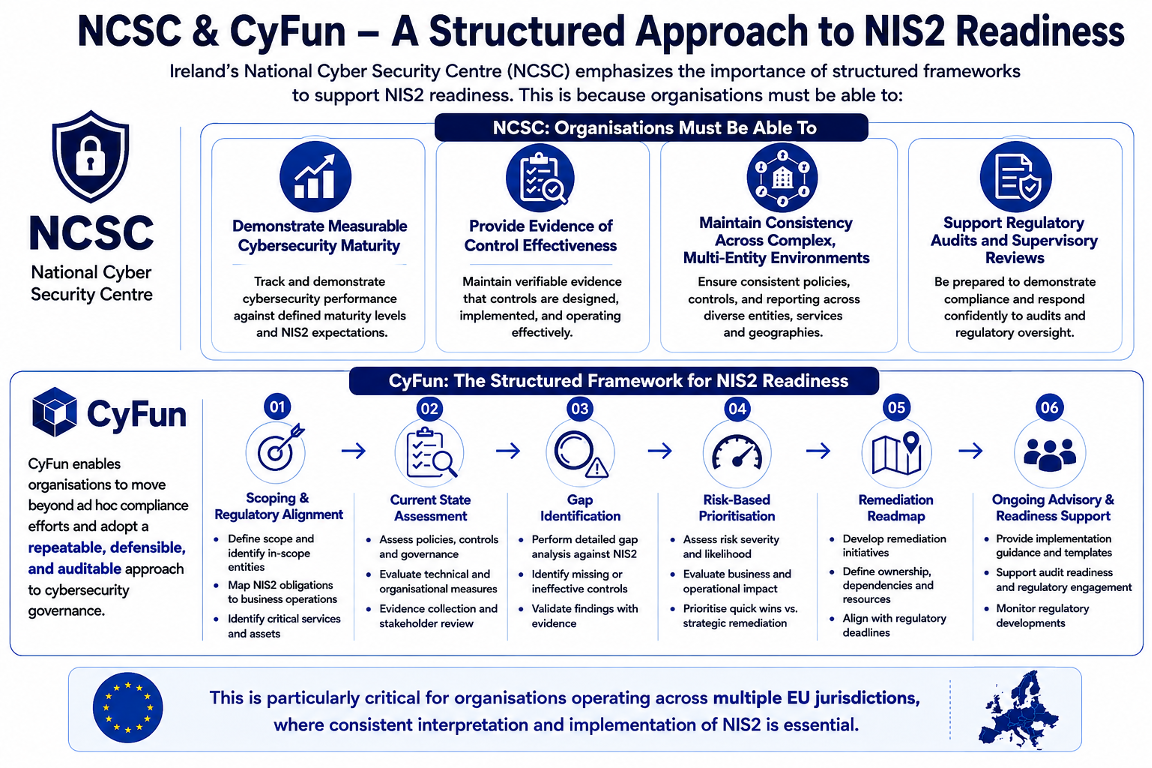
CyFun can give organisations a structured reference point for assessing cybersecurity measures, prioritising improvement and building evidence of implementation. When used within NIS2 Consulting, it can help a NIS2 Consultant organise assessment activities around defined cybersecurity measures while connecting findings to remediation priorities and business risk. Its maturity-oriented structure can also help organisations move beyond a one-time gap review towards repeatable assessment and improvement. For organisations operating across several EU Member States, CyFun can form part of a consistent internal methodology, while applicable national NIS2 legislation and competent-authority requirements should still be assessed separately.
· Establishes a structured governance framework aligned with the NIS2 Directive, enabling clear accountability and demonstrable compliance
· Defines a formal, business-aligned cybersecurity strategy tailored to organisational risk profile and regulatory obligations
· Embeds a risk-based approach to cybersecurity management, ensuring resources are prioritised against the most critical threats
· Strengthens cyber resilience through repeatable processes for incident response, recovery, and continuous improvement
· Enhances third-party and supply chain risk management in line with NIS2 requirements, reducing exposure from external dependencies
· Provides auditable evidence and reporting structures to support regulatory inspections, board oversight, and ongoing compliance assurance
Effective NIS2 readiness can strengthen cybersecurity governance, risk management, incident preparedness and management oversight while helping organisations address applicable regulatory obligations. The Directive requires essential and important entities to implement appropriate and proportionate cybersecurity risk-management measures, covering areas including incident handling, business continuity, supply-chain security and other specified controls. NIS2 Compliance Services can help organisations convert these requirements into defined actions, responsibilities, evidence and remediation priorities. A structured approach also gives leadership clearer visibility of cybersecurity risks and progress towards the requirements that apply to the organisation.
Frequently Asked Questions
A NIS2 maturity assessment evaluates your organisation’s cybersecurity capabilities against the requirements of the NIS2 Directive, providing a structured view of readiness and areas for improvement.
Yes. Ireland is required to transpose the NIS2 Directive into national law, and organisations operating in scope must comply with its requirements.
Regulators expect organisations to demonstrate not just compliance, but measurable cybersecurity maturity and effective risk management practices.
CyFun provides a structured framework that translates NIS2 requirements into measurable domains, enabling consistent assessment, benchmarking, and improvement.
No, but ISO 27001 alignment can support NIS2 compliance. A maturity assessment helps identify how your current controls align with both.
Organisations should begin assessing their readiness immediately, as regulatory expectations and supervisory activities are increasing across the EU.
The scope of NIS2 Compliance Services depends on an organisation’s regulatory position, operating environment and existing cybersecurity maturity. Support may include applicability and scope review, current-state assessment, cybersecurity gap analysis, risk prioritisation, remediation planning, governance review and implementation guidance. Kelmac Group®’s NIS2 Consulting can help organisations translate applicable requirements into practical actions and evidence while maintaining a clear distinction between consulting support and the responsibilities of regulators, competent authorities and independent conformity-assessment activities where applicable.
A NIS2 Consultant helps an organisation understand applicable NIS2 requirements and develop a structured approach to readiness and compliance. This can include assessing current cybersecurity measures, identifying gaps, reviewing governance and responsibilities, prioritising remediation and supporting implementation planning. The consultant can also help connect regulatory requirements with existing cybersecurity and risk-management practices. Legal applicability, regulatory interpretation and supervisory requirements should be considered in the context of the national legislation implementing NIS2 in the relevant EU Member State.
Yes. CyFun can provide a structured basis for assessing cybersecurity measures and maturity. Belgium’s Centre for Cybersecurity describes CyFun as a framework that can support implementation of NIS2 cybersecurity requirements, with different assurance levels reflecting progressively broader control requirements. When used for a NIS2 CyFun Maturity Assessment outside Belgium, organisations should also consider the national legislation, regulatory guidance and supervisory arrangements applicable in each EU Member State in which they operate.