Detecting…
LoginProtect your organisation’s information assets, strengthen cybersecurity governance and establish a structured Information Security Management System aligned with ISO/IEC 27001:2022. Kelmac Group provides end-to-end ISO 27001 consulting services, supporting organisations through ISMS design, implementation, documentation, risk management, internal audit, certification readiness and continual improvement.
ISO/IEC 27001:2022 is an internationally recognised standard for establishing, implementing, maintaining and continually improving an Information Security Management System, commonly referred to as an ISMS. The standard provides a risk-based framework for managing information security across people, processes and technology. It helps organisations protect the confidentiality, integrity and availability of information while addressing cybersecurity risks, legal obligations, contractual requirements and stakeholder expectations.
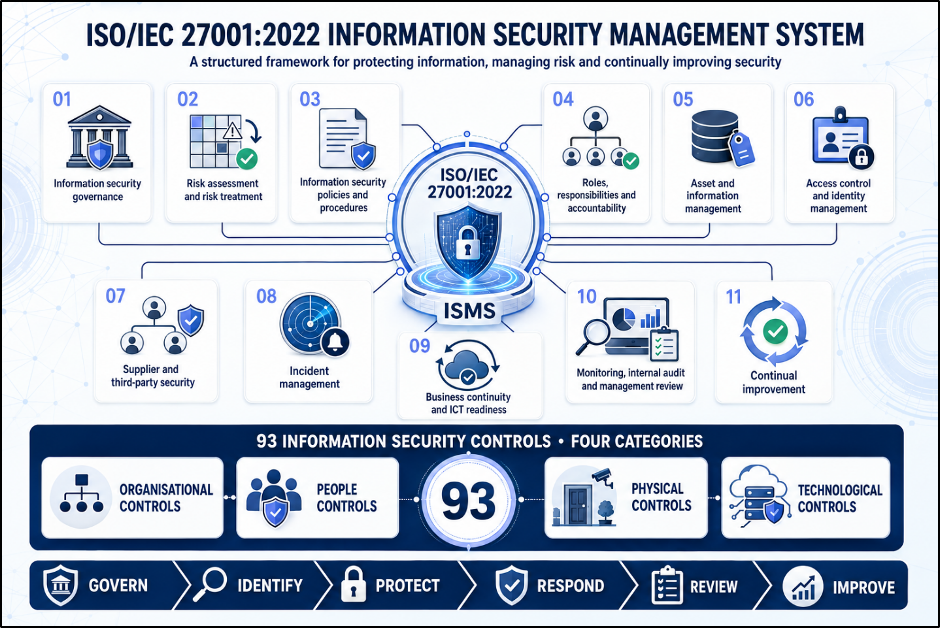
ISO 27001:2022 requires organisations to establish a structured management system covering areas such as:
Implementing ISO 27001 involves more than producing policies or completing a compliance checklist. Organisations must establish an ISMS that reflects their business context, information security risks, regulatory obligations and operational environment.
ISO 27001 consulting support helps organisations correctly interpret the requirements of the standard, design proportionate controls and create the evidence required for certification.
Kelmac Group’s ISO 27001 consultants help organisations:
Define the ISMS scope and organisational boundaries
Understand internal and external information security issues
Identify relevant interested parties and compliance obligations
Establish information security governance arrangements
Conduct information security risk assessments
Develop risk treatment plans
Select applicable Annex A controls
Prepare the Statement of Applicability
Develop required policies, procedures and records
Define measurable information security objectives
Implement operational and technical controls
Conduct internal audits
Support management reviews
Address nonconformities and corrective actions
Prepare for Stage 1 and Stage 2 certification audits
Professional consulting support can reduce implementation delays, avoid unnecessary documentation and help ensure that the ISMS is practical, effective and aligned with the organisation’s business objectives
ISO 27001 can be implemented by organisations of any size, sector or geographical location. It is particularly valuable for organisations that process sensitive, confidential, regulated or business-critical information, including:
Technology and software companies
Cloud and managed service providers
Financial services organisations
Healthcare organisations
Government and public-sector bodies
Professional services firms
Telecommunications providers
Educational institutions
Data processors and outsourcing providers
Manufacturing and engineering companies
Small and medium-sized enterprises
Multinational organisations
ISO 27001 certification may be required where organisations need to:
Demonstrate information security assurance to customers
Meet contractual or tender requirements
Strengthening cybersecurity governance
Reduce the risk of data breaches and operational disruption
Improve supplier and third-party assurance
Support regulatory compliance
Enter new markets
Improve customer and investor confidence
Establish a repeatable security management framework
Kelmac Group follows a structured, risk-based and business-focused methodology for ISO 27001 implementation and certification readiness.
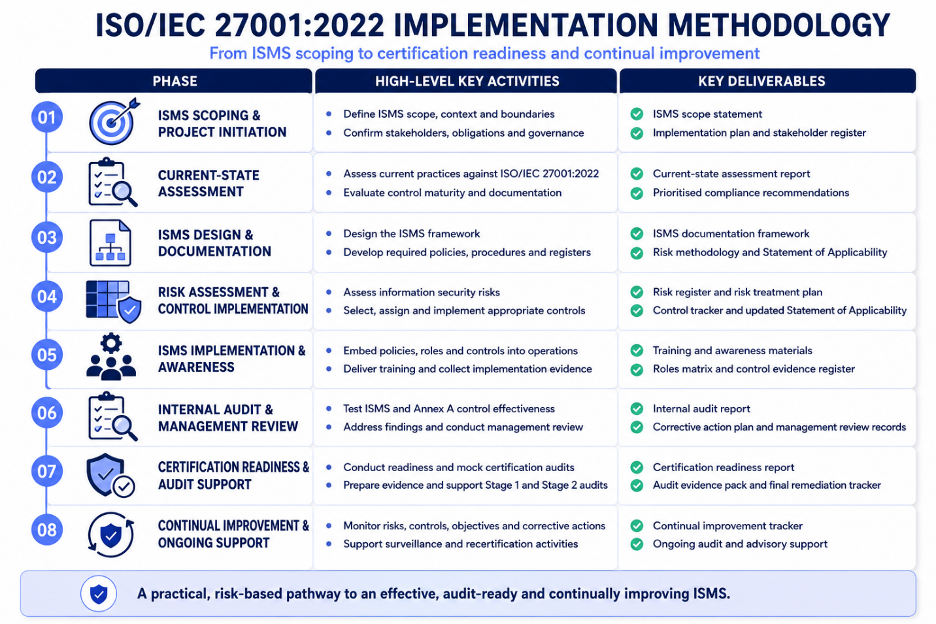
Kelmac Group provides practical, structured and implementation-focused ISO 27001 consulting services tailored to the organisation’s size, risk profile, sector and business objectives.
Risk-Based and Business-Focused: We design the ISMS around your organisation’s actual information security risks rather than applying unnecessary or generic controls.
End-to-End Consulting Support: Our services can cover the entire ISO 27001 journey, from initial scoping and risk assessment through to internal audit and certification support.
Practical Documentation: We develop policies, procedures, registers and templates that are proportionate, usable and aligned with your operational environment.
Evidence-Focused Approach: We help organisations demonstrate that controls are not only documented but also implemented, monitored and supported by appropriate evidence.
Integration with Existing Frameworks: Where relevant, we help align ISO 27001 with existing cybersecurity, privacy, quality, business continuity and risk management frameworks.
Certification Readiness Support: We prepare management, employees and control owners for certification-body interviews, evidence reviews and audit activities.
Continual Improvement: Our support can continue beyond certification to help maintain the ISMS, prepare for surveillance audits and respond to changing threats, technologies and business requirements.
ISO 27001 implementation involves establishing and operating an ISMS that meets the requirements of the standard. Certification is an independent assessment performed by an accredited certification body to confirm that the ISMS conforms to ISO/IEC 27001:2022.
The implementation period depends on the organisation’s size, complexity, scope, existing security maturity, resource availability and certification objectives. A smaller organisation with established controls may require less time than a large or complex organisation starting without formal ISMS.
ISO 27001 certification is generally voluntary. However, it may become a contractual, customer, tender, supplier-assurance or market-access requirement.
The Statement of Applicability identifies which ISO 27001 Annex A controls are applicable to the organisation. It also explains why controls have been included or excluded and describes their implementation status.
No. ISO 27001 applies across the defined ISMS scope and involves leadership, human resources, procurement, legal, compliance, facilities, operations, technology teams and other relevant business functions.
ISO 27001 does not prescribe a fixed set of technologies. Organisations must select appropriate controls based on their risks, operational requirements and business context.
Yes. ISO management system standards use a compatible structure, allowing organisations to integrate information security with quality, business continuity, privacy and other management systems.
Kelmac Group can support ISMS implementation, internal audit and certification readiness. The formal certification decision must be made independently by an accredited certification body.
The organisation must continue operating and improving its ISMS. Certification bodies normally perform periodic surveillance audits, followed by a recertification audit at the end of the certification cycle.