Data Privacy Officer as a Service (DPOaaS)
Kelmac Group’s DPO as a Service provides organisations with access to an experienced, independent Data Protection Officer without the cost and complexity of recruiting a full-time internal resource. Our outsourced DPO service helps organisations meet their obligations under the General Data Protection Regulation, strengthen privacy governance and manage data protection risks through ongoing, practical and commercially focused support. The service can be tailored for organisations that are legally required to appoint a DPO, as well as businesses that choose to appoint one voluntarily to improve accountability, customer confidence and regulatory readiness.
DPO as a Service, also known as DPOaaS or an outsourced Data Protection Officer service, enables an external privacy professional to perform the statutory and advisory functions of a DPO under a service contract. The external DPO works with senior management, legal, compliance, information security, human resources, procurement, marketing and operational teams to oversee the organisation’s data protection framework.
Depending on the agreed scope, Kelmac Group’s DPO as a Service may include:
Acting as the formally appointed Data Protection Officer
Advising management and employees on GDPR obligations
Monitoring compliance with data protection laws and internal policies
Reviewing privacy risks associated with projects, systems and suppliers
Advising on Data Protection Impact Assessments
Supporting personal data breach assessment and response
Monitoring data subject rights processes
Reviewing Records of Processing Activities
Supporting privacy notices, policies and procedures
Liaising with supervisory authorities
Acting as a contact point for individuals
Delivering privacy awareness and role-based training
Providing regular compliance reporting to senior management
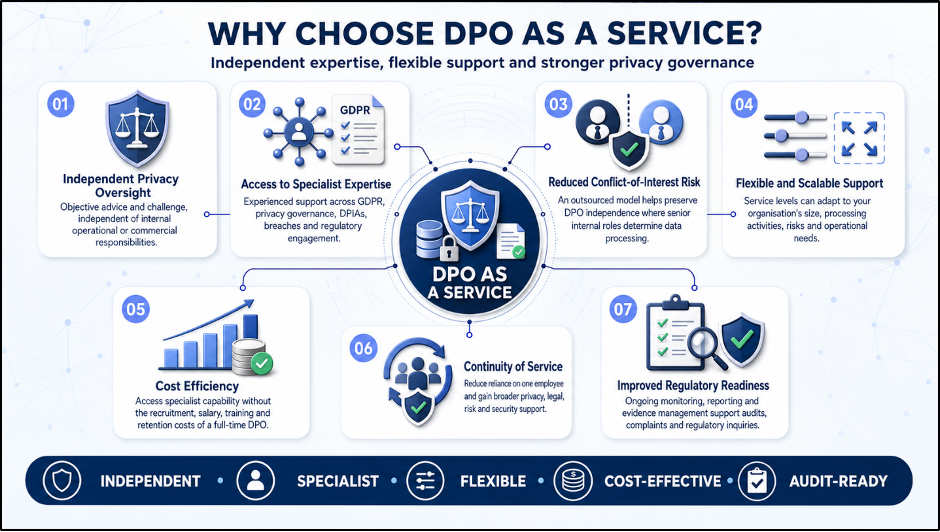
An outsourced DPO can provide access to specialist expertise while maintaining the independence required for the role.
A Data Protection Officer provides independent oversight, advice and monitoring in relation to an organisation’s data protection obligations. Under the GDPR, the DPO’s statutory tasks include informing and advising the organisation, monitoring compliance, advising on Data Protection Impact Assessments and cooperating with the relevant supervisory authority. A DPO may be appointed externally under a service contract, provided the requirements concerning expertise, independence, resources and absence of conflicts of interest are maintained.
Articles 37–39 of the GDPR establish the conditions for appointing a DPO, the position the DPO must hold within the organisation and the minimum tasks associated with the role. An organisation must appoint a DPO where:
The processing is carried out by a public authority or public body, except courts acting in their judicial capacity
Its core activities involve regular and systematic monitoring of individuals on a large scale
Its core activities involve large-scale processing of special-category data
Its core activities involve large-scale processing of personal data relating to criminal convictions and offences
Organisations that appoint a DPO must publish the DPO’s contact details and communicate those details to the relevant supervisory authority. A DPO must be involved properly and in a timely manner in matters relating to personal data protection. The organisation must provide the DPO with sufficient access, resources and support to perform the role effectively.
The DPO must be able to:
Operate independently
Report directly to the highest management level
Perform the role without receiving instructions regarding the outcome of their advice
Avoid roles or responsibilities that create a conflict of interest
Access relevant information, systems, records and stakeholders
Maintain appropriate professional knowledge of data protection law and practice
The DPO advises and monitors, but responsibility for GDPR compliance remains with the controller or processor.
Appointing an outsourced DPO provides a practical alternative to recruiting and retaining a full-time internal specialist.
Supporting GDPR Compliance Through Independent DPO Oversight
Effective GDPR Compliance requires ongoing governance rather than a one-time documentation exercise. An outsourced DPO can advise management on data protection obligations, monitor compliance activities, provide input into DPIAs and help organisations maintain visibility of privacy risks and improvement priorities. The DPO must retain the independence required by the role and should report to the organisation’s highest management level. Responsibility for compliance, however, remains with the controller or processor rather than transferring to the DPO.
GDPR Gap Analysis
A GDPR Gap Analysis provides a structured review of an organisation’s existing privacy arrangements to identify areas where governance, documentation, processes or operational practices may require improvement. The review can consider areas such as accountability, records of processing activities,transparency information, data subject rights, processor arrangements, data retention, security, personal data breaches, international transfers and DPIA processes, according to the agreed scope.
Findings can then be prioritised according to regulatory exposure, privacy risk and operational impact. A GDPR Gap Analysis does not itself establish or certify compliance; it provides a practical basis for remediation planning and improvement.
GDPR Compliance Assessment and Gap Assessment
A GDPR Compliance Assessment evaluates how an organisation’s current privacy governance and data-processing practices align with applicable GDPR requirements. Depending on scope, the assessment can examine policies, responsibilities, processing records, lawful bases, transparency arrangements, individual-rights procedures, DPIAs, supplier controls, breach management and supporting evidence.
A GDPR Gap Assessment can form part of this process by identifying differences between current arrangements and the organisation’s applicable requirements or target state. The resulting findings can help management determine priorities, assign responsibilities and establish a proportionate remediation plan. Where a DPO is appointed, assessment activities should be structured so that the independence and statutory position of the DPO are preserved.
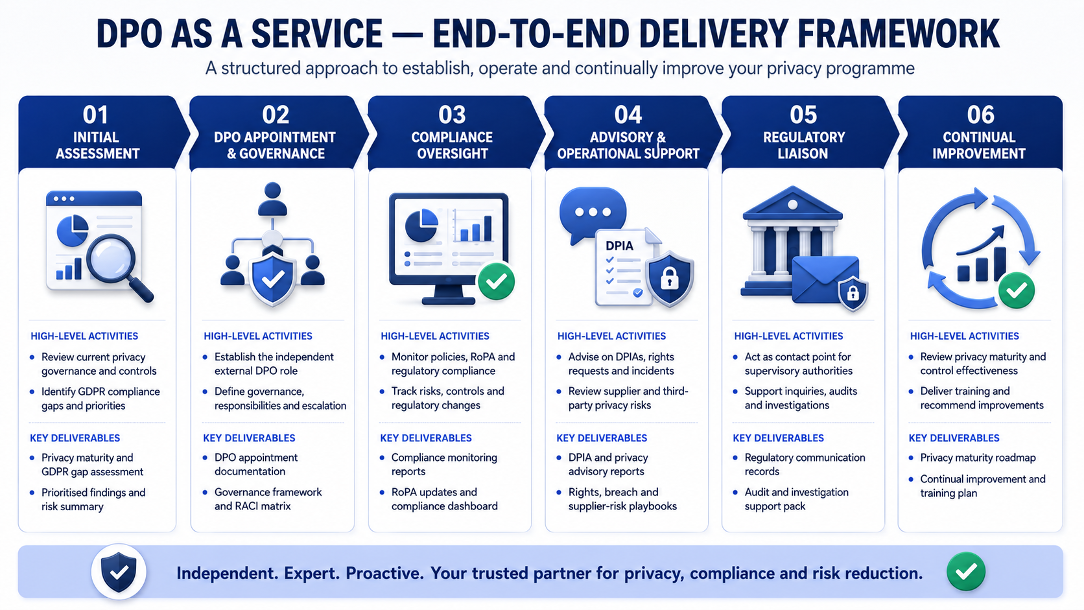
Our approach is structured, risk-based, and aligned with leading privacy and security frameworks.
A well-implemented DPO function delivers more than regulatory compliance; it strengthens organisational resilience and trust.
Enhanced Compliance: Ensure alignment with GDPR and related EU data protection regulations.
Risk Reduction: Identify and mitigate privacy risks before they result in incidents or fines.
Improved Governance: Establish clear accountability and structured oversight of data processing activities.
Customer Trust: Demonstrate commitment to protecting personal data, enhancing brand reputation.
Operational Efficiency: Streamline processes related to data subject rights, breach management, and documentation.
Regulatory Confidence: Be prepared for audits, investigations, and regulatory inquiries
Kelmac Group provides practical and independent DPO support tailored to the organisation’s risk profile, operating model and regulatory environment.
Independent and Conflict-Free: The DPO service is structured to protect the independence of the role and ensure that privacy advice can be provided objectively
Experienced Privacy Professionals: Our consultants combine knowledge of data protection law, privacy governance, information security, risk management and regulatory compliance.
Risk-Based Delivery: We prioritise activities according to the nature of the personal data, processing scale, affected individuals and potential impact on their rights and freedoms.
Practical Business Advice: Our recommendations are designed to support compliance while recognising commercial, operational and technical realities.
Integration with Existing Frameworks: The DPO service can align with existing GDPR, ISO 27001, ISO 27701, cybersecurity, risk, audit and governance programmes.
Clear Management Reporting: We provide structured reporting so senior management can understand privacy risks, priorities, dependencies and required decisions.
Scalable Service Model: Support can be tailored from periodic advisory oversight to a comprehensive managed DPO function.
Frequently Asked Questions
A DPO is mandatory where the organisation meets one of the conditions in Article 37 GDPR, including certain public-sector processing, large-scale regular and systematic monitoring, or large-scale processing of special-category or criminal-offence data. Where appointments are not legally mandatory, an organisation may still choose to appoint a DPO voluntarily. Once formally designated as a DPO under GDPR, the organisation should ensure that the role, independence and responsibilities are properly respected.
Yes. GDPR allows the DPO role to be fulfilled under a service contract by an individual or an external organisation, provided the required expertise, accessibility, independence and conflict-of-interest safeguards are maintained.
GDPR does not prescribe one specific qualification. The DPO should be appointed based on professional qualities, particularly expert knowledge of data protection law and practice, and the ability to perform the statutory tasks of the role. The appropriate level of expertise should reflect the sensitivity, scale and complexity of the organisation’s processing activities.
Kelmac Group provides a named or managed DPO resource that works with your internal stakeholders, reports to senior management and delivers the agreed advisory, monitoring, assurance and regulatory-contact activities. The arrangement is documented through defined responsibilities, communication channels, reporting arrangements and service priorities.
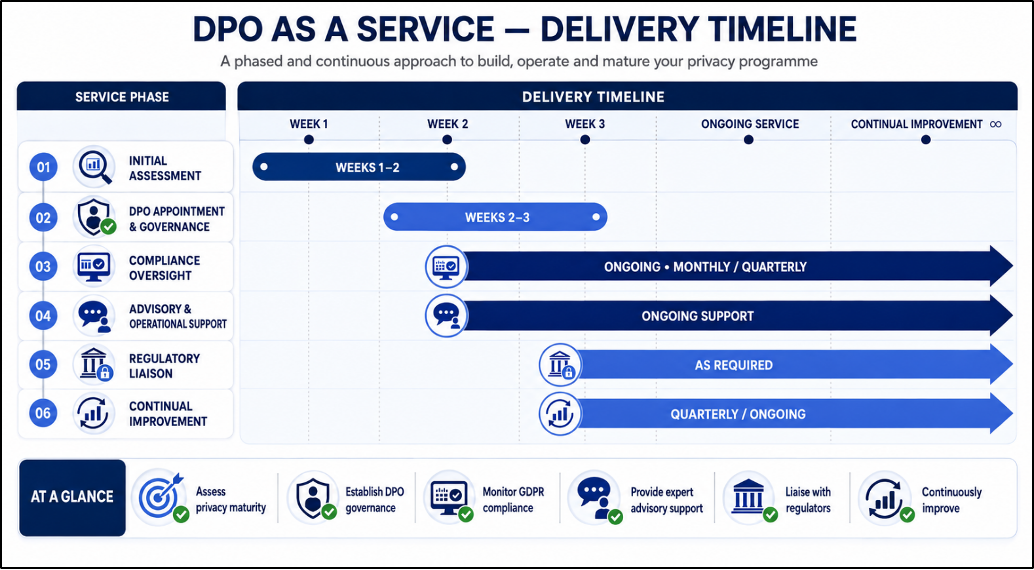
An outsourced DPO can generally be mobilised faster than recruiting a permanent internal resource. The exact timeline depends on organisational complexity, legal entities, processing activities, conflict checks and the availability of key information and stakeholders
Yes. The DPO should be involved promptly in personal data incidents and can advise on risk assessment, notification obligations, communication with affected individuals and engagement with the supervisory authority. Operational responsibility for investigating, containing and managing the incident remains with the organisation
Organisations that appoint a DPO pursuant to Article 37 GDPR must publish the DPO’s contact details and communicate them to the relevant supervisory authority. In Ireland, the DPC maintains a register of notified DPO contact details.
A GDPR Gap Analysis reviews an organisation’s current privacy governance, documentation and operational practices to identify areas that may require improvement against applicable GDPR requirements. Its scope can include accountability arrangements, processing records, privacy notices, individual-rights processes, DPIAs, processor management, breach procedures, retention and other relevant areas. The findings can be prioritised to create a structured remediation plan. A gap analysis is an assessment and improvement activity; it should not be described as GDPR certification.
A GDPR Compliance Assessment is a structured evaluation of how an organisation manages applicable data protection requirements. It can review governance, policies, processing activities, lawful bases, transparency, individual rights, risk management, supplier arrangements, security and supporting evidence. The exact assessment scope should reflect the organisation’s processing activities and regulatory context. Assessment findings can then inform remediation, governance improvements and ongoing privacy-management priorities.
Yes. EU GDPR arrangements and UK regulatory guidance allow the DPO role to be fulfilled externally under a service contract, provided the applicable requirements for the position are met. The DPO must be able to perform the role independently, have appropriate expertise and resources, avoid conflicts of interest and have access to the organisation’s highest management level.
Kelmac Group® can position its service for organisations in Ireland and the UK, provided this accurately reflects its confirmed delivery capability. For Ireland and other EU jurisdictions, the relevant GDPR framework and national supervisory context should be considered. For UK organisations, the service should address the UK GDPR and applicable UK data protection requirements. The regulatory frameworks should not be presented as identical, even where many DPO principles and requirements are closely aligned.