European Union Digital Operational Resilience Act (DORA) Regulation
Assess your organisation’s compliance with the EU Digital Operational Resilience Act, identify critical ICT and third-party risk gaps, and develop a practical roadmap for achieving and maintaining DORA compliance. The Digital Operational Resilience Act (DORA) establishes harmonised requirements designed to strengthen digital operational resilience across the EU financial sector. Since 17 January 2025, financial entities within scope have been required to address areas including ICT risk management, ICT-related incident management and reporting, digital operational resilience testing, ICT third-party risk and information-sharing arrangements. A structured DORA compliance approach helps organisations connect these regulatory requirements with existing governance, cybersecurity, business continuity and technology-risk practices.
The Digital Operational Resilience Act (DORA) is an EU regulation designed to strengthen the digital operational resilience of the financial sector. It requires regulated financial organisations to demonstrate that they can prevent, withstand, respond to and recover from cyberattacks, technology failures and other Information and Communication Technology (ICT) disruptions. DORA has applied since 17 January 2025 and covers a wide range of organisations, including banks, insurance companies, investment firms, payment institutions, pension providers, crypto-asset service providers and certain ICT third-party service providers.
A DORA gap analysis helps your organisation assess its current ICT risk management, cybersecurity and operational resilience arrangements against the requirements of the Digital Operational Resilience Ac
The assessment identifies where existing policies, processes, contracts, technologies and controls meet DORA requirements and where compliance gaps, weaknesses or missing evidence remain. It provides a structured understanding of your organisation’s current level of DORA readiness.
A structured ICT Risk Assessment provides evidence of how effectively an organisation identifies, protects against and manages technology-related risks affecting financial services. Within a DORA gap analysis, this means reviewing ICT governance, policies, controls, systems, continuity arrangements and supporting evidence against applicable requirements.
The assessment can expose weaknesses that may not be apparent from policy documentation alone, including inconsistent control implementation, unclear ownership, inadequate recovery arrangements or gaps in third-party oversight. Findings can then be prioritised according to regulatory significance, operational impact and the organisation’s risk profile.
DORA ICT Risk Management
DORA ICT Risk Management requires financial entities to maintain a structured framework for identifying, managing and monitoring ICT risk. The framework should support the protection and resilience of ICT systems, information assets and technology-dependent business services while establishing clear governance and accountability.
A DORA assessment can examine the design and implementation of ICT risk controls, including governance, asset and risk identification, protection and prevention measures, detection, response and recovery arrangements. Kelmac Group® can use the findings to help organisations identify control gaps, establish remediation priorities and develop a practical implementation roadmap aligned with applicable DORA requirements.
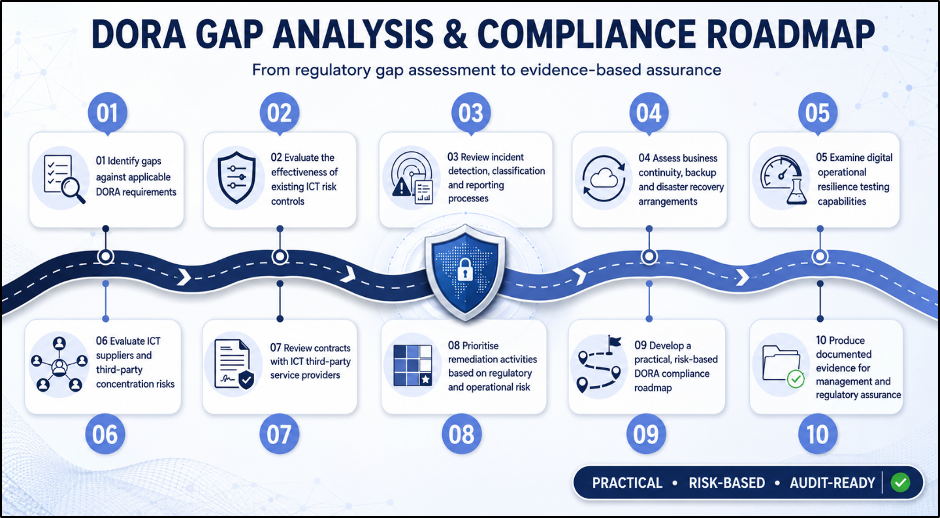
Without a structured gap analysis, organisations may overlook critical compliance obligations, weaknesses in ICT governance or dependencies on technology suppliers. These gaps can increase exposure to operational disruption, regulatory scrutiny, financial loss and reputational damage.
Kelmac Group’s DORA Gap Analysis and Readiness Assessment helps financial entities understand their compliance position, identify priority risks and establish a clear roadmap towards sustainable DORA compliance and enhanced digital operational resilience.
DORA applies to a broad range of EU financial entities, including:
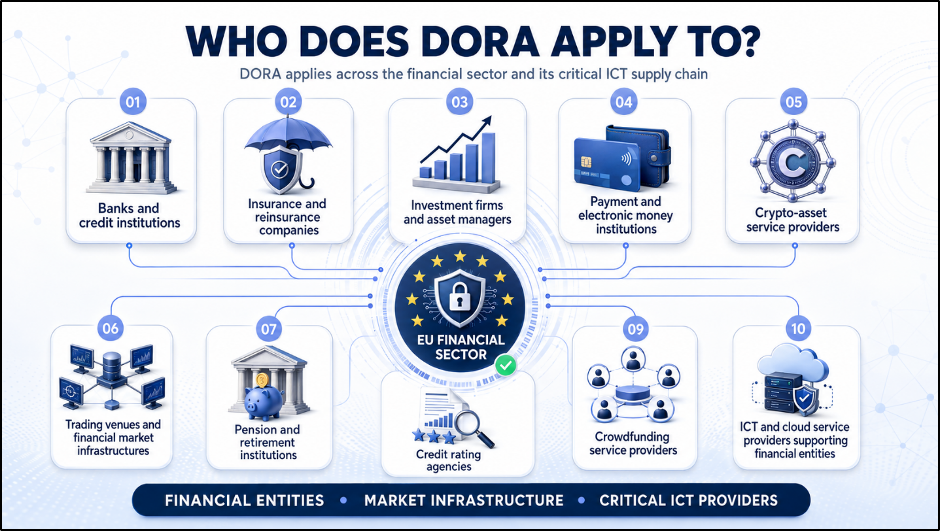
The precise obligations may vary depending on the organisation’s type, size, risk profile and role within the financial services ecosystem. A DORA applicability assessment can help establish which regulatory requirements apply to your organisation.
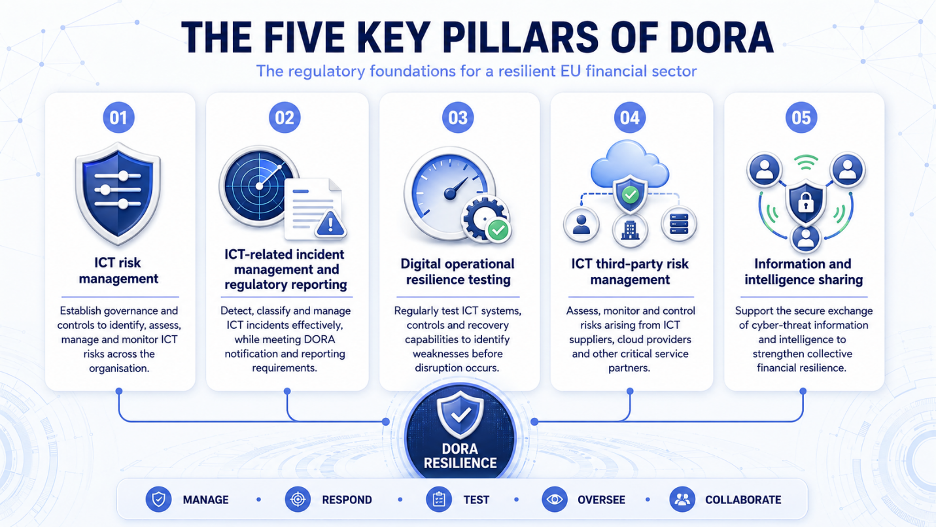
Effective DORA operational resilience depends on these regulatory areas operating as an integrated system rather than as separate compliance activities. ICT risk governance informs incident management and testing, while testing outcomes can expose weaknesses requiring remediation. Third-party oversight extends the organisation’s risk-management approach to external ICT dependencies.
Together, these requirements are intended to strengthen a financial entity’s ability to withstand, respond to and recover from ICT disruption. Organisations should therefore consider how governance, cybersecurity controls, continuity arrangements, testing, incident processes and supplier oversight collectively support their digital operational resilience objectives.
DORA Third-Party Risk Management
DORA Third-Party Risk Management addresses the risks financial entities face when relying on external providers for ICT services. Under DORA, using an ICT third-party service provider does not transfer the financial entity’s responsibility for meeting its regulatory obligations. Third-party dependencies therefore need to be identified, assessed, governed and monitored as part of the organisation’s ICT risk management framework.
A DORA third-party risk assessment can consider provider due diligence, contractual arrangements, services supporting critical or important functions, concentration risk, information-security expectations, monitoring, audit and access provisions, business continuity dependencies and exit arrangements. Financial entities are also required to maintain a register of information concerning contractual arrangements with ICT third-party service providers
Kelmac Group conducts an independent and structured assessment of your organisation’s existing ICT governance, cybersecurity, operational resilience and third-party risk management arrangements against applicable DORA requirements. Our consultants review both documented controls and their practical implementation to determine whether your organisation can demonstrate effective and sustainable compliance.
KelmacGroup methodology is aligned with regulatory expectations and industry’s best practices.
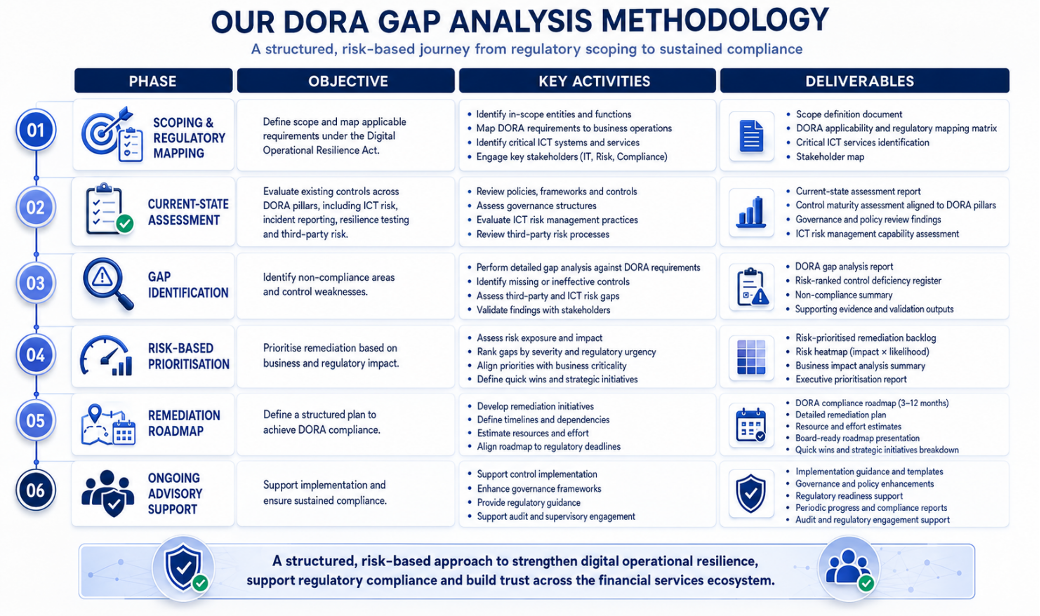
Kelmac Group®’s assessment methodology can incorporate DORA ICT Risk Management, ICT third-party dependencies and operational resilience requirements within the wider gap-analysis process. This allows findings to be considered in their operational context rather than treated as isolated compliance observations.
The resulting assessment can help management understand where documented arrangements and implemented controls differ from applicable DORA requirements, what evidence is available to demonstrate implementation and which remediation activities warrant priority. The objective is to establish a clear, risk-based path from current-state assessment through remediation planning and ongoing compliance support.
Kelmac Group combines information security, risk management, regulatory compliance, auditing and management-system expertise to provide a practical approach to digital operational resilience. Our approach is:
● Risk-based: Findings are prioritised according to operational and regulatory significance.
● Evidence-focused: We assess whether controls are implemented and supported by demonstrable evidence.
● Business-aligned: Recommendations consider your organisation’s size, complexity and critical services.
● Implementation-oriented: We provide practical actions rather than simply identifying weaknesses.
● Framework-integrated: Existing ISO 27001, business continuity, cybersecurity and supplier-risk controls are considered.
● Management-focused: Reporting is designed to support informed decisions, accountability and regulatory assurance.
Frequently Asked Questions
DORA has applied since 17 January 2025 to financial entities and other organisations that fall within its scope. Applicable organisations must be able to demonstrate that the required governance, risk management, testing, incident reporting and ICT third-party controls are operating effectively.
No. ISO 27001 can provide a strong foundation, but organisations must assess and address DORA-specific obligations.
The duration depends on the organisation’s size, complexity, number of legal entities, ICT environment and availability of evidence. Kelmac Group should provide a tailored scope after an initial consultation.
Evidence may include policies, ICT risk registers, asset inventories, incident records, testing reports, supplier contracts, continuity plans, recovery tests, governance minutes and registers of information.
Certain ICT providers may be directly affected by DORA’s oversight framework, while other suppliers will face contractual, assurance and information requirements from regulated financial-sector customers.
Yes. We provide end-to-end support, from gap analysis through to full compliance and operational resilience maturity.
DORA ICT Risk Management refers to the governance, policies, processes, controls and supporting arrangements financial entities use to manage ICT risk under the Digital Operational Resilience Act. DORA requires financial entities to maintain an ICT risk management framework appropriate to their circumstances, subject to applicable proportionality and specific regulatory requirements.
DORA Third-Party Risk Management concerns the identification, assessment, governance and monitoring of risks arising from the use of ICT third-party service providers. Financial entities remain responsible for their DORA obligations when using external ICT services and must address requirements concerning contractual arrangements, due diligence, monitoring and relevant ICT dependencies.
DORA requires financial entities to identify, classify and adequately document ICT-supported business functions, information assets and ICT assets, together with their roles and dependencies, and to identify sources of ICT risk. A structured ICT risk assessment can therefore form an important part of demonstrating how these requirements are implemented and maintained.
No. Financial entities using ICT services remain responsible for compliance with their obligations under DORA. This makes appropriate due diligence, contractual governance, monitoring and management of ICT third-party risk particularly important.